Bearlink by Beareye
Bearlink: sovereign TPRM software unifying compliance and supplier cyber risk
Bearlink is a French supplier risk management platform. It automates the collection and verification of compliance documents and manages regulatory due diligence. It is the only TPRM integrated into a complete automated Red Team platform (Beareye): each supplier’s cyber rating is produced by Beareye’s own engines, with no external partner.
- Document compliance
- Native cyber rating
- Developed in France
Endless chasing, and a cyber blind spot
Proving that your suppliers are compliant ties your teams up in reminders and spreadsheets: URSSAF social security certificates, Kbis company registration extracts, insurance, the French anti-corruption law (Sapin II), the French corporate duty of vigilance law, and now NIS2 and DORA. Meanwhile, nobody knows how secure your critical suppliers really are. These two blind spots are handled separately today, and badly.
What does Bearlink do for your suppliers?
| Building block | What you get |
|---|---|
| Third-party register | A single record per supplier, from onboarding to exit, segmented by criticality |
| Supplier portal | A space where the supplier uploads its documents and answers questionnaires, with automatic reminders |
| Document compliance | Certificates collected, tracked until expiry and archived |
| Due diligence | Sapin II, duty of vigilance, CSR, GDPR, NIS2 and DORA questionnaires; sanctions screening; IBAN checks |
| Native cyber rating | Each supplier’s cyber score as seen from outside, leaks, spoofing, alerts when it deteriorates |
| Management and reporting | Action plans, dashboards and reports by profile |
The only TPRM integrated into a complete automated Red Team platform
Most TPRM tools live apart, disconnected from the rest of risk management. Bearlink is the only TPRM integrated into a complete automated Red Team platform (Beareye). Supplier risk joins your attack surface, your vulnerabilities and the offensive validation of your defences, under one management view.
Standalone TPRM
Bearlink integrated into Beareye
- Compliance
- Native cyber rating
- Attack surface
- Automated Red Team
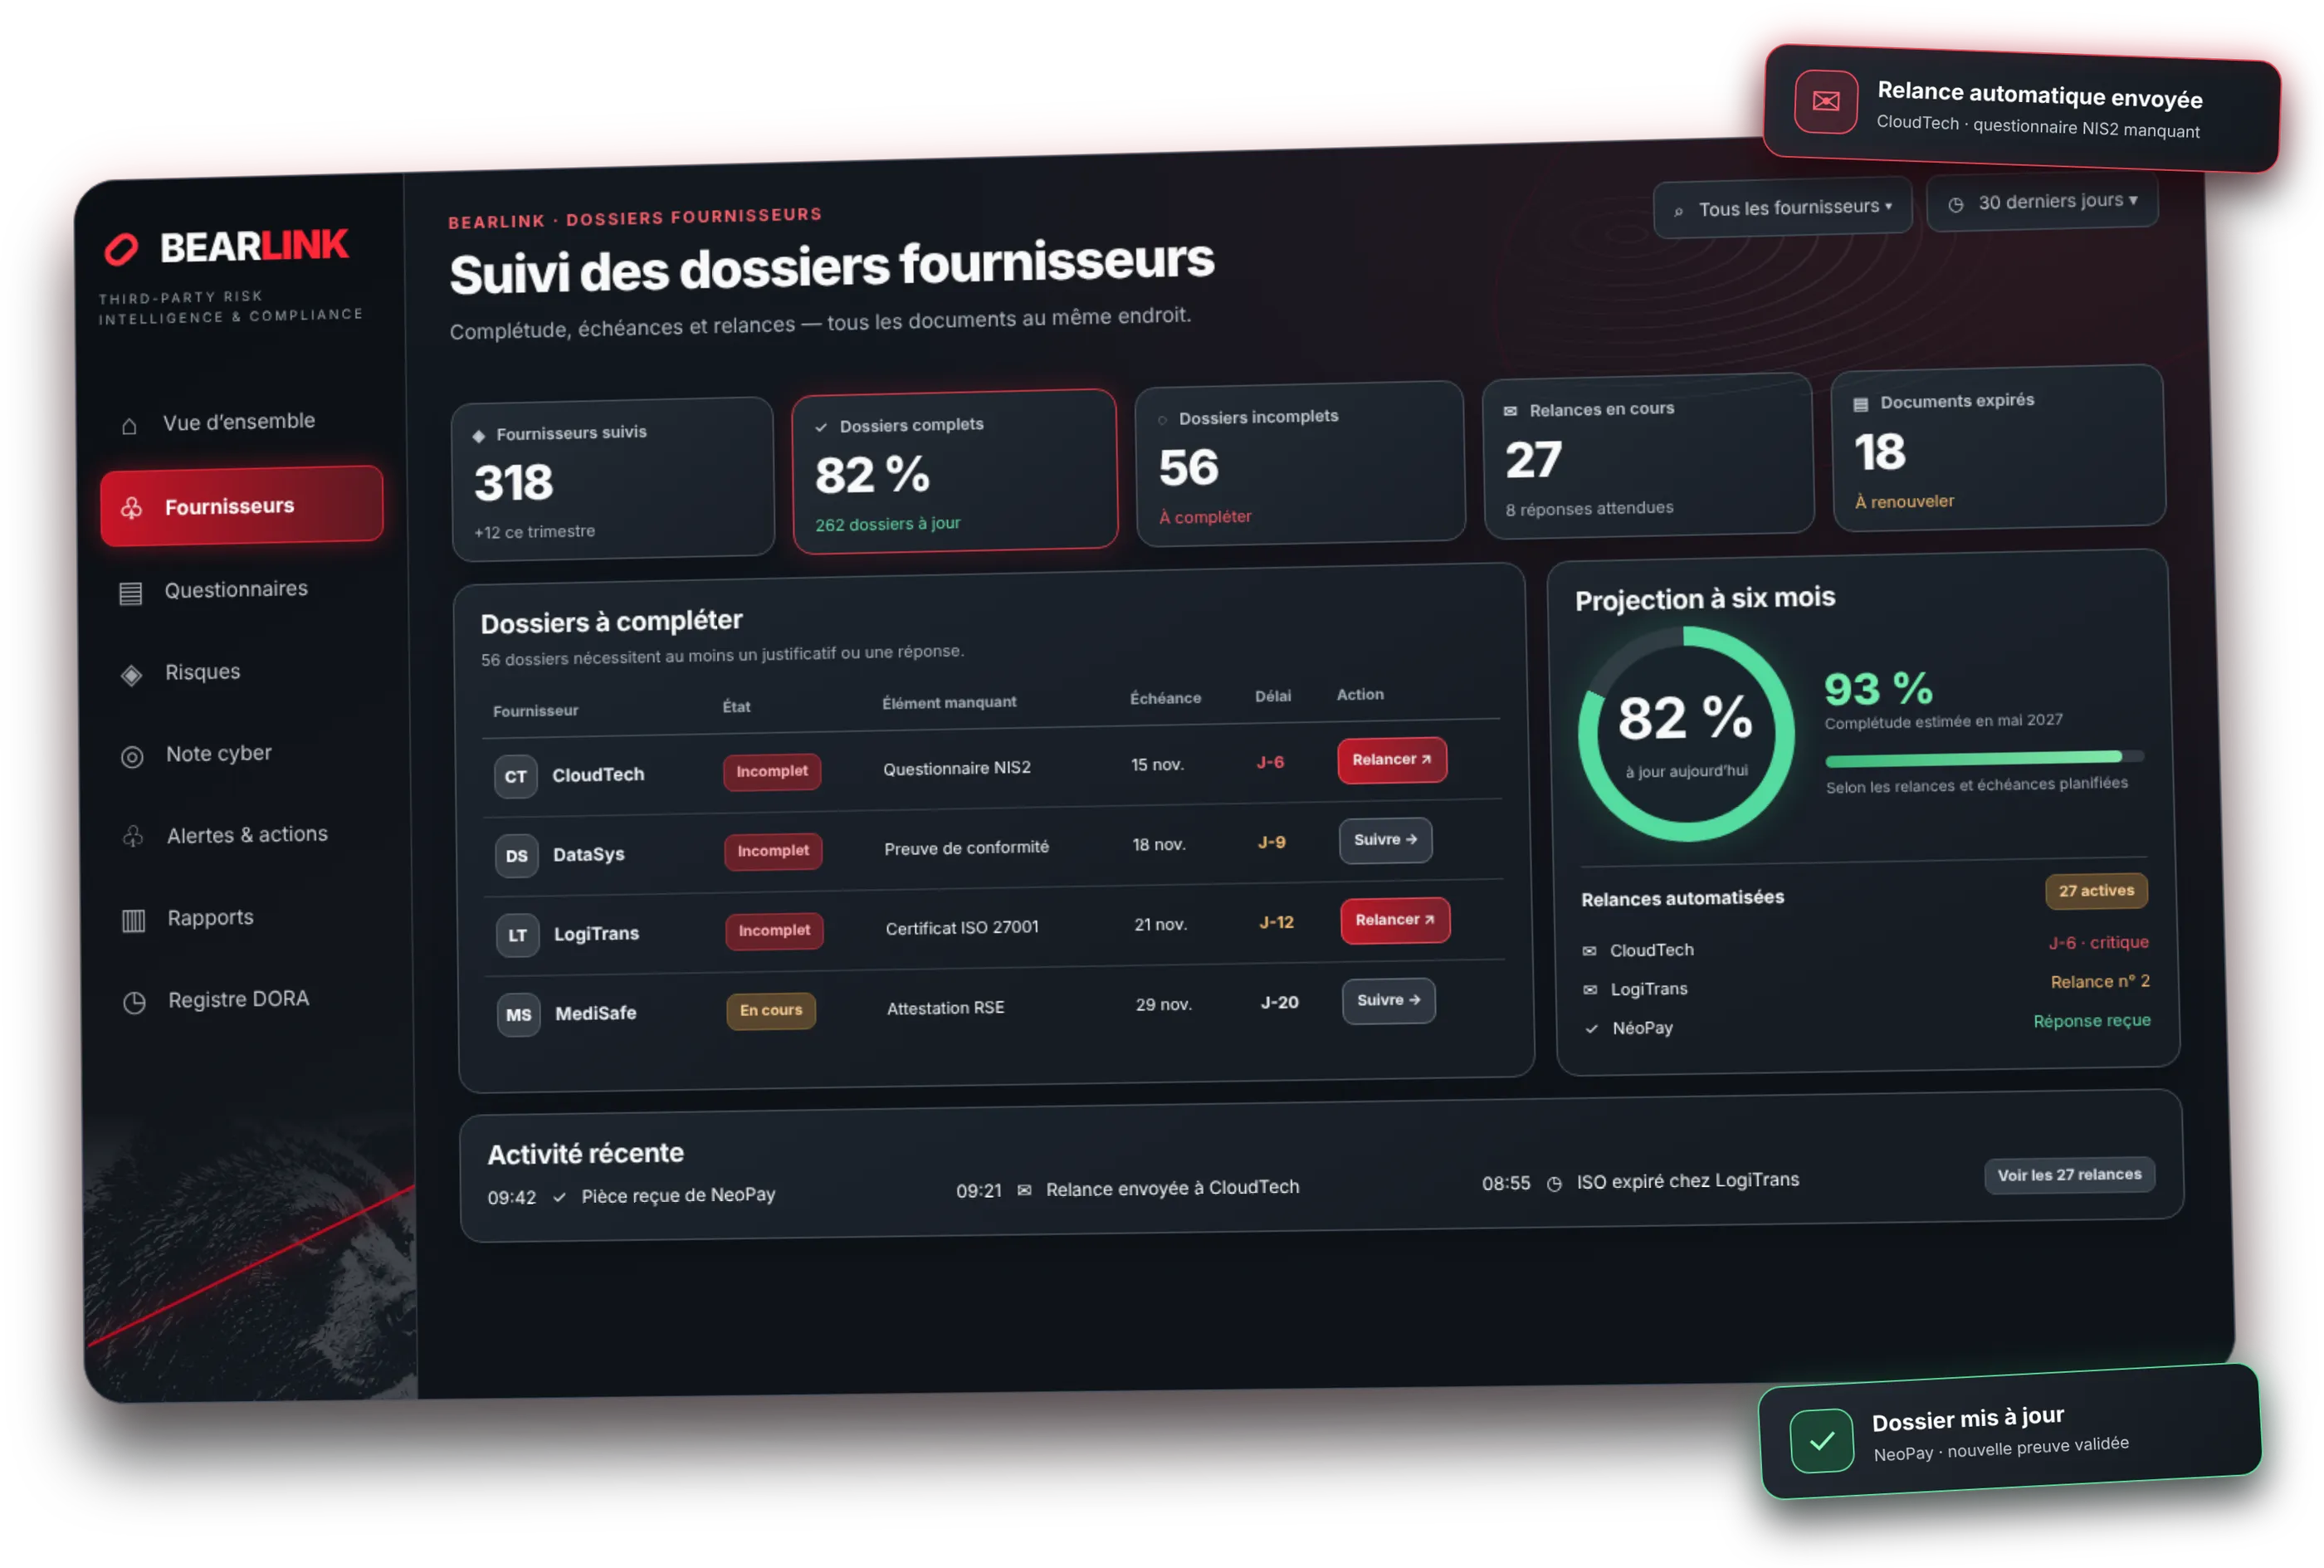
The real question: how many files will still be up to date in six months
A supplier compliance tool is only worth the share of files that are genuinely complete and up to date. Bearlink acts on that rate: a frictionless supplier portal, multichannel reminders, a dashboard of incomplete files. Completeness is not a detail; it is what actually protects you.
Which obligations apply to your suppliers?
| Obligation | What it requires regarding suppliers |
|---|---|
| Vigilance obligation (French Labour Code) | URSSAF certificate and company registration at signature, then every 6 months |
| Sapin II (French anti-corruption law) | Assess the integrity of third parties within the anti-corruption programme |
| Duty of vigilance (French corporate duty of vigilance law) | A plan covering suppliers and subcontractors, with regular assessment |
| NIS2 | Supply chain security among the expected measures |
| DORA | Control of ICT third-party service provider risk, register of information |
| GDPR | Check the guarantees provided by processors (Article 28) |
Bearlink, on its own or with the suite
| Mode | Entry point | What you get |
|---|---|---|
| Bearlink on its own | Procurement, Compliance | A complete TPRM, cyber included, without subscribing to the other modules |
| Extension for a Beareye customer | CISO | Extend exposure management to the supply chain, in the same tool |
| Through a partner MSSP | Partner | A supply chain offer provided by your service provider |
Frequently asked questions
What is a TPRM?
A TPRM (third-party risk management) tool manages the risks linked to third parties: suppliers, subcontractors, partners. It centralises document compliance, regulatory due diligence and risk assessment, including cyber risk.
What sets Bearlink apart from Aprovall or Provigis?
Bearlink covers document compliance as they do, but it is the only TPRM integrated into a complete automated Red Team platform. Its cyber rating is produced by Beareye’s engines, not imported from a partner, and supplier risk is managed alongside the rest of your exposure, not in a standalone tool.
Can Bearlink be bought without the rest of the suite?
Yes. Bearlink is sold under its own brand and can be bought on its own, without subscribing to the EASM, CAASM or CTI modules. A Beareye customer can also activate it in the same environment to extend its exposure management to its suppliers.
Does Bearlink provide legal advice?
No. Bearlink describes the obligations and provides the tools to track them. Legal interpretation and compliance decisions remain with your organisation and its advisers.
How does a supplier’s cyber rating work?
Bearlink assesses the supplier’s exposed attack surface from the outside, without asking it for anything: visible services, leaks, domain spoofing. The rating is updated continuously and raises an alert when it deteriorates. This assessment relies on Beareye’s EASM module.
Where is my suppliers’ data hosted?
Hosted in France on OVHcloud infrastructure certified ISO/IEC 27001. Technology developed in France, with no exposure to the US CLOUD Act.
How much does Bearlink cost?
Bearlink starts at €500 per year, excluding VAT. The exact amount depends on the scope covered and is set out in the quote.
See your suppliers the way an attacker sees them
Choose a sample of your suppliers. Bearlink presents their document compliance and their cybersecurity rating side by side, in a single meeting. The proof is made on your own third parties.