Beareye · Platform
Beareye: a sovereign cyber risk and exposure management platform
Beareye is a SaaS platform for unified cyber and third-party risk management, developed in France by BEAROPS. It centralises your external, internal, cloud and threat exposure, validates it as an attacker would through automated Red Teaming, then produces the action plan and the indicators that prove to your leadership that risk is going down.
- Developed in France
- Automated Red Teaming
- Data hosted by OVHcloud
Tools that don’t talk to each other, a risk you cannot prove
A CISO piles up scanners, one-off penetration tests and compliance spreadsheets that do not communicate. The result: blind spots, time-consuming manual correlation, and no simple answer when leadership asks whether risk has gone down. Beareye brings these sources together on the same data and in the same view.
A Command Center and four modules
Beareye is made up of a cross-cutting Command Center, included in every subscription, and four modules that can be purchased separately. The Command Center centralises vulnerabilities, the action plan, evidence and automated Red Teaming . The EASM , CAASM, CTI and Bearlink modules cover external exposure, internal exposure, threat intelligence and supplier risk.
| Building block | What it covers |
|---|---|
| Command Center | Vulnerabilities, action plan, tickets, KPIs, compliance, automated Red Teaming |
| EASM | External attack surface: assets, email, shadow IT, typosquatting |
| CAASM | Internal and cloud surface: AD, Azure, O365, GCP, IoT, segmentation |
| CTI | Intelligence: continuous OSINT monitoring , dark web monitoring , leaks, MITRE ATT&CK, CVE |
| Bearlink | Supplier risk: compliance and native cyber rating |
Discover, prioritise, validate, remediate
Beareye works in four stages. Discover external, internal and cloud exposure. Prioritise by real attack path rather than by a raw list of vulnerabilities. Validate exploitability through automated Red Teaming. Remediate with an action plan and tickets ( vulnerability management ), then replay to check that the fix holds.
-
Discover
Continuous inventory of exposed and internal assets.
-
Prioritise
Ranking by attack path and asset criticality.
-
Validate
Automated exploitation to confirm what is actually exploitable.
-
Remediate
Action plan, remediation tickets, replay after the fix.
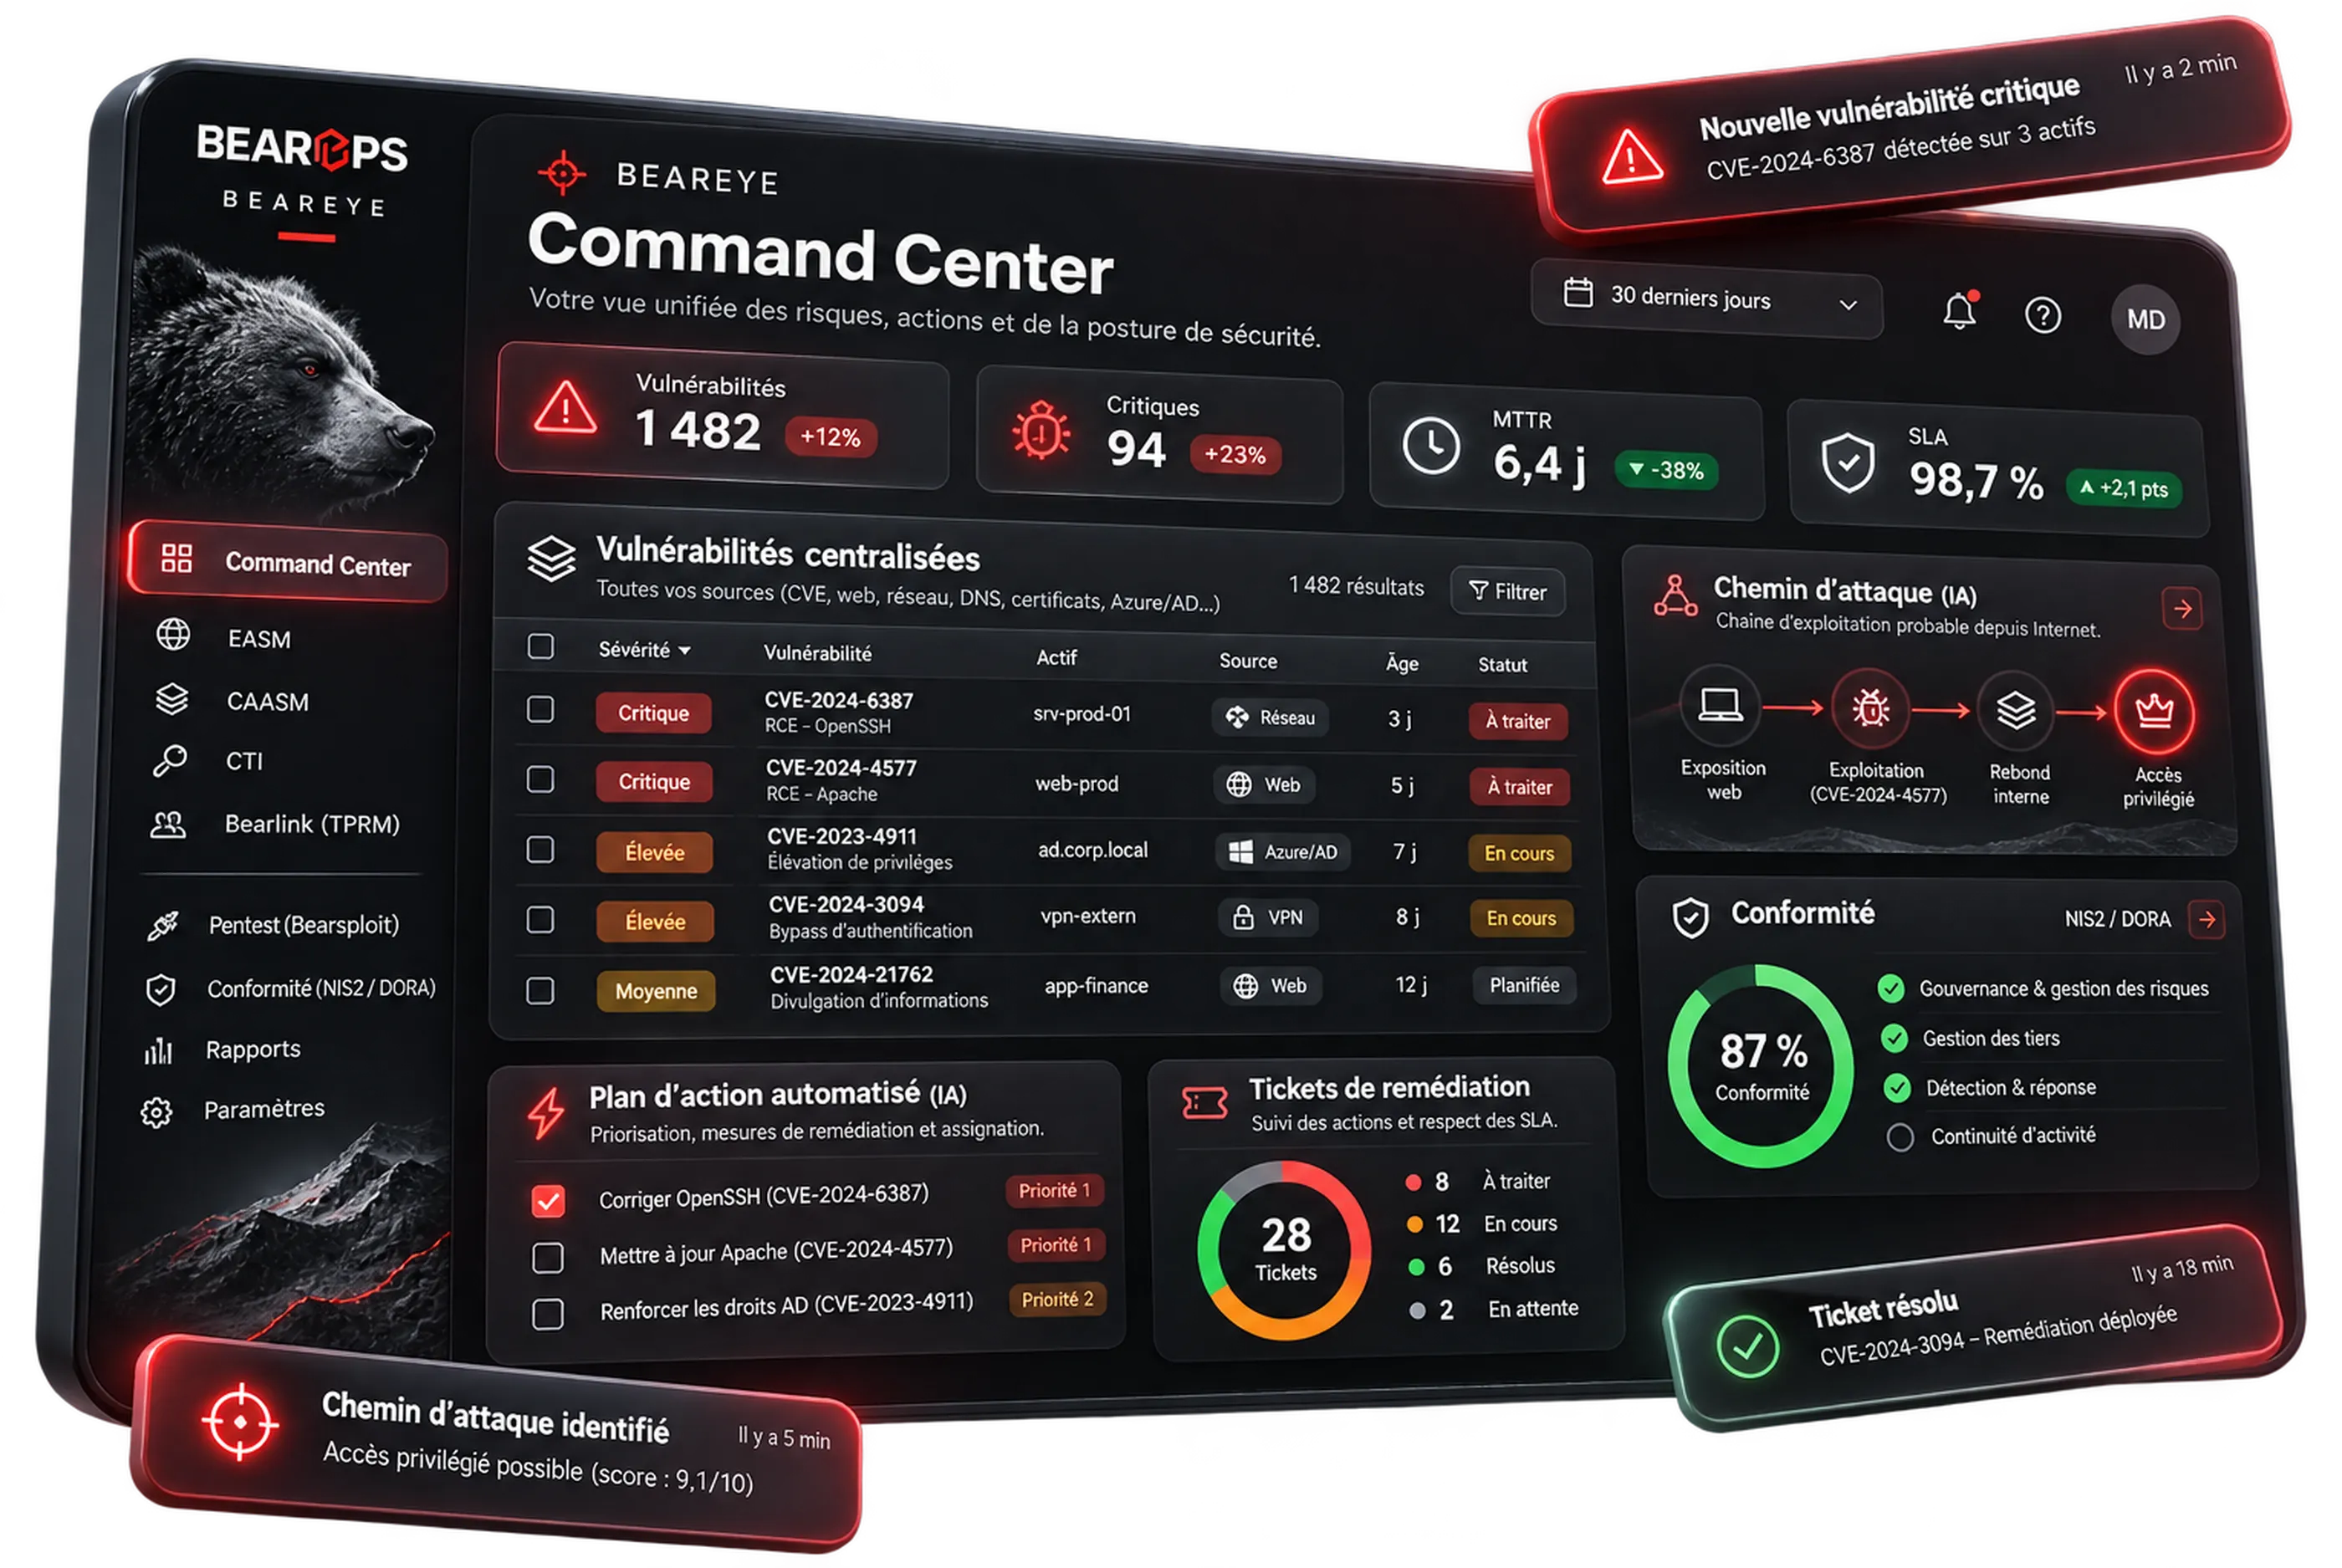
The Command Center, your single view
The Command Center is Beareye’s cross-cutting foundation. It centralises all vulnerabilities, the automated action plan, remediation tickets, MTTR and SLA indicators, tracking of NIS2 and DORA measures, and automated Red Teaming with its attack paths and emulated kill chain.
- Single view of vulnerabilities
- Automated action plan
- Remediation tickets
- MTTR and SLA KPIs
- Tracking of NIS2 and DORA measures
- Automated Red Teaming
- Executive committee reports
Connecting signals to reveal the real attack paths
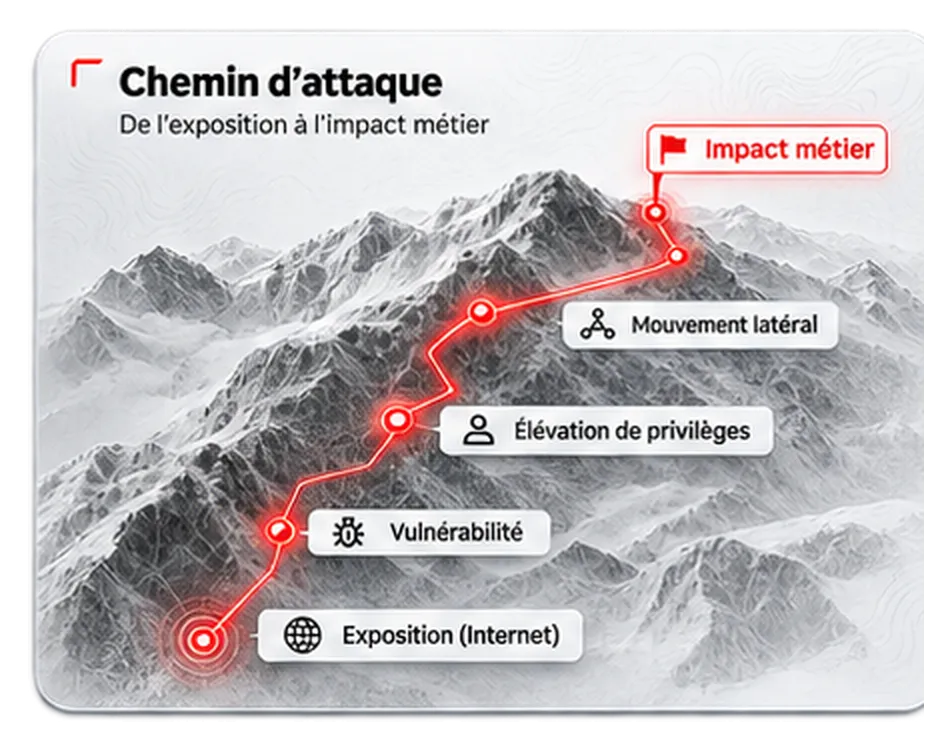
Beareye correlates its engines to link an exposed asset, a vulnerability, a leak and an access right into a single attack path. This correlation separates a theoretical vulnerability from a risk that is actually exploitable in your environment, and focuses remediation effort on what matters. This is the principle of continuous threat exposure management (CTEM) .
What Beareye changes in your context
| Context | What Beareye delivers |
|---|---|
| Sole CISO in an SME | One platform instead of several tools, a clear action plan, a report ready for leadership |
| CISO at a mid-sized industrial company | IT, OT and cloud exposure in one view, continuous proof that risk is going down |
| CISO at a large enterprise | Depth at the scale of hundreds of thousands of assets, integration with the existing ecosystem |
Does Beareye integrate with your SIEM and existing tools?
Beareye exposes an API and connects to the tools already in place, so that findings reach your teams’ workflow rather than yet another console.
How does Beareye help with NIS2 and DORA?
Beareye lets you industrialise the vulnerability assessments and continuous testing provided for in Article 25 of DORA , and track how weaknesses are remediated. It helps you prepare and document the measures expected under NIS2 . Beareye does not make you compliant: it produces the evidence.
-
NIS2 compliance
BEAROPS helps you prepare, document and demonstrate the risk management measures expected under NIS2. -
DORA compliance
BEAROPS helps you prepare, document and demonstrate your resilience testing and the monitoring of your ICT providers.
Developed in France, with no exposure to the CLOUD Act
Beareye: technology developed in France, with no exposure to the US CLOUD Act. Its data is hosted in France on OVHcloud infrastructure certified ISO/IEC 27001.
Evidence before claims
The Cyberscore analyses your own perimeter in 30 minutes.
Frequently asked questions
How does Beareye differ from a vulnerability scanner?
A scanner lists vulnerabilities without context. Beareye correlates them with actual exposure, validates which ones an attacker would exploit through automated Red Teaming, then replays after remediation. The goal is not to find more flaws, but to know which ones to fix first.
Does automated Red Teaming replace a penetration test?
No. Beareye’s automated Red Teaming keeps up the pressure between two audits, across the whole perimeter, and checks that remediations hold. The human penetration test remains useful and becomes more targeted. The two are complementary.
Is Beareye also suitable for SMEs?
Yes. An SME CISO, often working alone, gets a platform that replaces several tools and a report ready for leadership. A mid-sized company or a large enterprise uses it to manage an IT, OT and cloud surface at a larger scale.
How does Beareye integrate with my SIEM?
Beareye exposes an API and sends its findings to your SIEM, your ticketing tool and your CMDB, so that they reach your teams’ workflow.
What if we already have a SOC or an MSSP?
The SOC detects what is happening. Beareye reduces what could happen, upstream. The two are complementary. Beareye is also distributed by MSSPs to their own customers.
How much does Beareye cost?
Beareye starts at €10,000 per year, excluding VAT. The exact amount depends on the scope covered and is set out in the quote.
Measure your exposure in 30 minutes
The Beareye Cyberscore analyses your external attack surface and presents the priority exposures, during a 30-minute session with a BEAROPS engineer.